
In 2022 the National Bank of Romania (BNR) issued the regulation on the framework for cyber resilience testing, TIBER-RO1 (Regulation no. 6 of 3 May 2022). It is based on TIBER-EU, the framework published by the European Central Bank in 2018.
The regulation applies to the operators of financial market infrastructures overseen by the National Bank of Romania and to credit institutions designated as critical participants in those infrastructures. Other participants that are not designated as critical may run a TIBER-RO test voluntarily.
According to the BNR, the entities required to run TIBER-RO tests are:
Financial market infrastructure operators:
- BNR-IPF - ReGIS, SaFIR
- Transfond - SENT
- The central securities depository - RoClear
Credit institutions designated as critical participants in 2022:
- ING Bank N.V., Amsterdam - Bucharest Branch
- Raiffeisen Bank S.A.
- Banca Comercială Română S.A.
- UniCredit Bank S.A.
- BRD - Groupe Société Générale S.A.
- Citibank Europe p.l.c. Dublin - Romania Branch
- Banca Transilvania S.A.
They must run TIBER-RO tests at least once every 3 years.
The first test had to be carried out within 3 years of the regulation entering into force, i.e. by 3 May 2025.
Tests are performed on the production infrastructure, procedures, staff and outsourced services that support the critical functions of the tested entity.
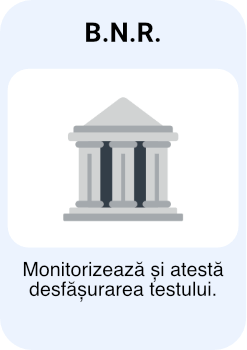
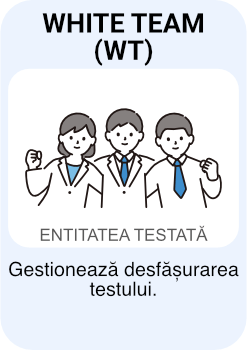
Parties involved in TIBER-RO testing
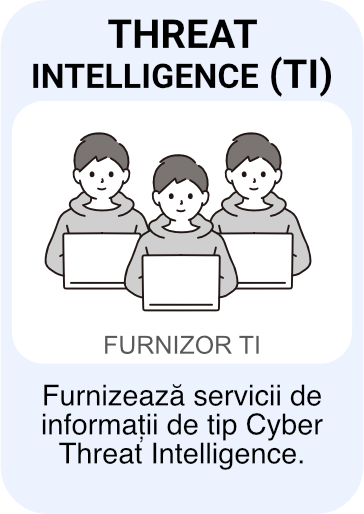
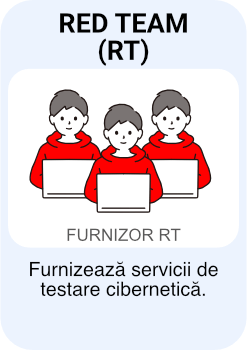
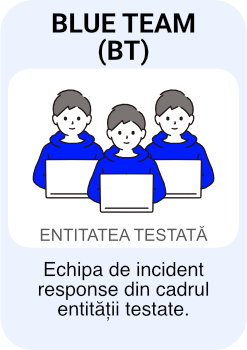
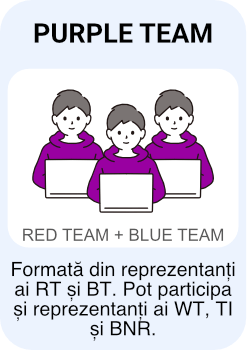 (test replay)
Testing is carried out in a controlled way by a Red Teaming provider, based on a Cyber Threat Intelligence report specific to the tested entity.
The tests simulate, in a controlled way, cyber attacks by technologically advanced and persistent attackers - including organised crime groups or state actors - that could affect the availability, integrity and confidentiality of the resources supporting the entity's critical functions, using the tools, methods and techniques of those attackers, in order to verify and improve the cyber resilience of the tested entity.
How a TIBER-RO test runs
A TIBER-RO test runs over a long period, and the Red Team works in stages to limit the likelihood of detection by the Blue Team. The minimum total duration is 25 weeks, broken down into the phases shown in the chart below.
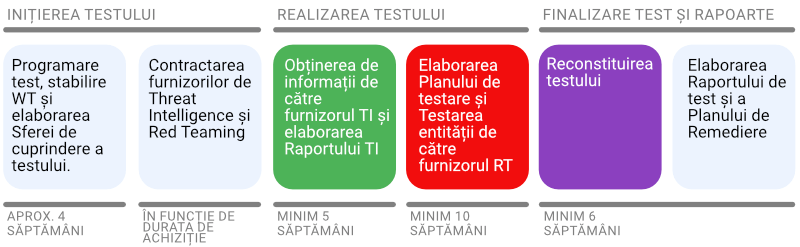
The BNR is involved in every phase of the test:
- It monitors the tests throughout
- It provides guidance to the White Team for the whole duration of the test
- It approves the test documentation
- It attests that the test was carried out in line with the regulation
- It monitors the implementation of the measures in the Remediation Plan
1) TIBER = Threat Intelligence Based Ethical Red Teaming
https://www.bnro.ro/apage.aspx?pid=404&actId=333255
https://www.ecb.europa.eu/pub/pdf/other/ecb.tiber_eu_framework.en.pdf
Security Engineer · All Safe